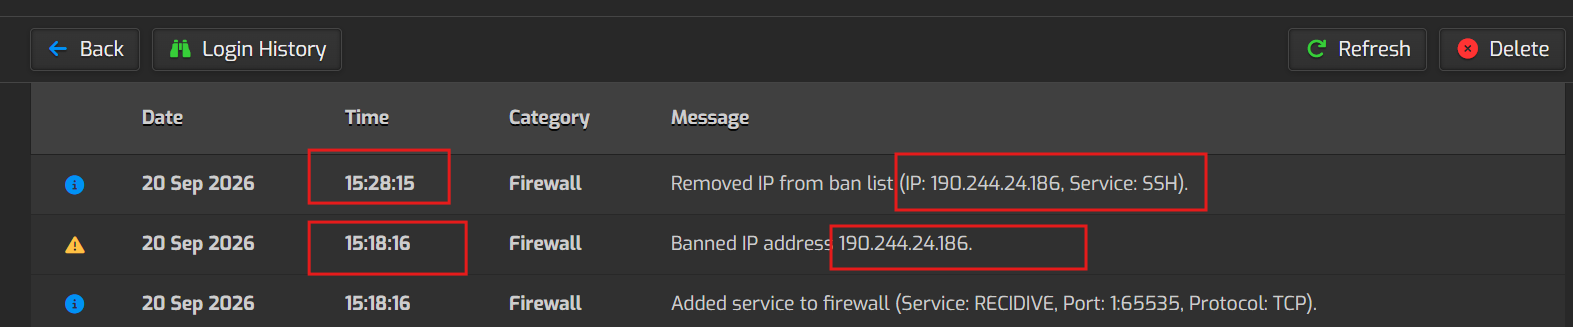
I am just wondering if this fail2Ban behaviour is normal? A ban only lasts for about 10 minutes after which it is removed from the ban list. I have set the default bantime = 864000 but I am surprised the ban still only lasts for 10 minutes.
/etc/fail2ban/jail.conf-# ignorecommand = /path/to/command
/etc/fail2ban/jail.conf-ignorecommand =
/etc/fail2ban/jail.conf-
/etc/fail2ban/jail.conf-# “bantime” is the amount of time tha
t a host is banned, integer in seconds or
/etc/fail2ban/jail.conf-# time abbreviation format (m - minut
es, h - hours, d - days, w - weeks, mo - months, y - years).
/etc/fail2ban/jail.conf-# This is to consider as an initial t
ime if bantime.increment gets enabled.
/etc/fail2ban/jail.conf:bantime = 10m
/etc/fail2ban/jail.conf-
/etc/fail2ban/jail.conf-# A host is banned if it has generate
d “maxretry” during the last “findtime”
–
/etc/fail2ban/jail.conf-
/etc/fail2ban/jail.conf-[apache-badbots]
/etc/fail2ban/jail.conf-# Ban hosts which agent identifies sp
ammer robots crawling the web
/etc/fail2ban/jail.conf-# for email addresses. The mail outpu
ts are buffered.
/etc/fail2ban/jail.conf-port = http,https
/etc/fail2ban/jail.conf-logpath = %(apache_access_log)s
/etc/fail2ban/jail.conf:bantime = 48h
/etc/fail2ban/jail.conf-maxretry = 1
/etc/fail2ban/jail.conf-
–
/etc/fail2ban/jail.conf-# 2. Increase dbpurgeage defined in f
ail2ban.conf to e.g. 648000 (7.5 days)
/etc/fail2ban/jail.conf-# to maintain entries for failed l
ogins for sufficient amount of time
/etc/fail2ban/jail.conf-[recidive]
/etc/fail2ban/jail.conf-
/etc/fail2ban/jail.conf-logpath = /var/log/fail2ban.log
/etc/fail2ban/jail.conf-banaction = %(banaction_allports)s
/etc/fail2ban/jail.conf:bantime = 1w
/etc/fail2ban/jail.conf-findtime = 1d
/etc/fail2ban/jail.conf-
–
/etc/fail2ban/jail.conf-# access log of the website with HTTP
auth
/etc/fail2ban/jail.conf-logpath = %(apache_access_log)s
/etc/fail2ban/jail.conf-blocktype = RETURN
/etc/fail2ban/jail.conf-returntype = DROP
/etc/fail2ban/jail.conf-action = %(action_)s[blocktype=
%(blocktype)s, returntype=%(returntype)s,
/etc/fail2ban/jail.conf- actionstart_o
n_demand=false, actionrepair_on_unban=true]
/etc/fail2ban/jail.conf:bantime = 1h
/etc/fail2ban/jail.conf-maxretry = 1
/etc/fail2ban/jail.conf-findtime = 1
–
/etc/fail2ban/jail.local-enabled = true
/etc/fail2ban/jail.local-filter = recidive
/etc/fail2ban/jail.local-action = hestia[name=RECIDIVE]
/etc/fail2ban/jail.local-logpath = /var/log/fail2ban.log
/etc/fail2ban/jail.local-maxretry = 5
/etc/fail2ban/jail.local-findtime = 86400
/etc/fail2ban/jail.local:bantime = 864000
/etc/fail2ban/jail.local-
/etc/fail2ban/jail.local-#Uncomment and add your IPs and or d
omains to the Whitelist
Ok, as you said, you had set the default bantime = 864000. I thought you had changed it manually.
That’s the default bantime configured in jail.conf
In the screenshot you posted, the jail used to ban the IP is SSH, defined by Hestia in jail.local, and it doesn’t have a scpecific bantime, so it is using the default (10 minutes).
The bantime = 864000 is only defined in the RECIDIVE jail and the IP will be banned for 10 days if it was already banned 5 times in a day.